Workspaces and roles
The right people change the right rules
Role-based access for business rules, arranged the way your business is. Finance owns finance decisions, operations owns theirs, and nobody publishes a change they should not.
Incoming request
evaluatingWho can publish a change to the credit limit rules?
- The credit controller is an author, so they can create a draft and test it.
- They cannot publish, so the Active version is untouched.
- The head of credit is a publisher, reviews the draft and its test traces.
- The head of credit publishes the new version.
Answer, with the reason
The change goes live only after someone with the publisher role has looked at it. Procurement members never see the Finance workspace, and the earlier version is kept in case anyone needs to check what the limit was before.
Sound familiar?
Letting the business own rules is great, until anyone can change anything
Moving rules out of code puts them in the hands of the people who know them. It also raises a fair question from IT and audit: who is allowed to change what?
Everyone can see everything
Procurement's supplier checks sit next to finance's credit rules. People scroll past decisions that are not theirs, and sometimes edit them.
No line between drafting and publishing
The person who makes a change is the same person who puts it live. There is no second pair of eyes.
Access decided by who asked last
New starters get admin because it was easier. Leavers keep access because nobody remembered.
The quiet cost
What loose access quietly costs
- A well-meant change to someone else's rule causes a problem nobody saw coming.
- Audit questions who approved a change and there is no clear answer.
- IT refuses to let the business own rules at all, and you are back to dev tickets.
Before and after
From one shared space to clear ownership
Today
- All decisions sit in one place for everyone.
- Anyone who can edit can also put changes live.
- Access is granted ad hoc and rarely reviewed.
- IT is nervous about handing over control.
With Condexa
- Each area of work has its own workspace.
- Authors draft changes; publishers put them live.
- Members are invited with a role that fits their job.
- IT keeps control of access while the business owns the rules.
How you get there
How workspaces and roles work
- 1
Create a workspace per area
Set up workspaces for finance, procurement, sales or any area of work. Each holds its own workflows, lookup tables and lists.
- 2
Invite members with a role
Invite people and give them a role, for example viewer, author, publisher or owner. Screens only show what each person is allowed to do.
- 3
Sign in securely
People sign in through a secure identity provider, so access follows the same rules as the rest of your business systems.
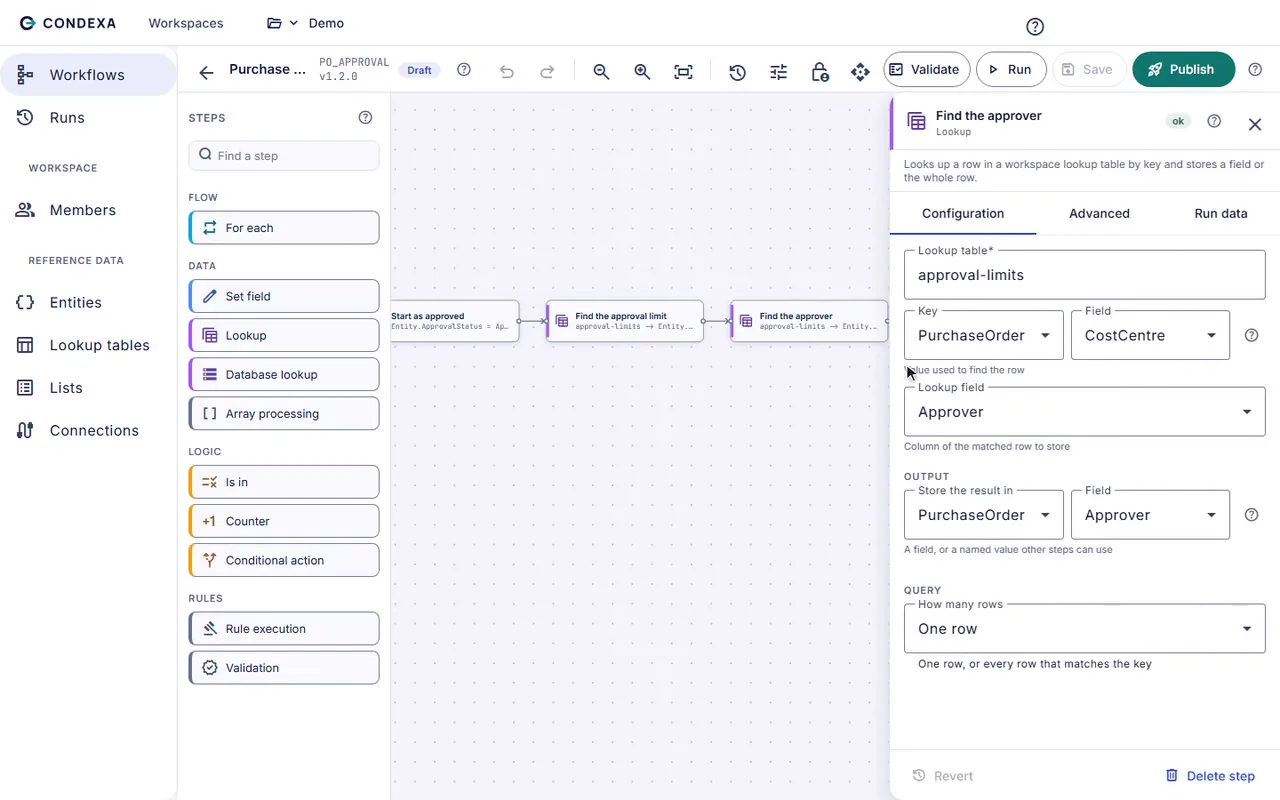
A worked example
Worked example: a credit limit change with two sets of eyes
A credit controller wants to raise the default credit limit for new trade accounts in the Finance workspace.
The rules, in plain English
- R1The credit controller is an author, so they can create a draft and test it.
- R2They cannot publish, so the Active version is untouched.
- R3The head of credit is a publisher, reviews the draft and its test traces.
- R4The head of credit publishes the new version.
Condexa answers
The change goes live only after someone with the publisher role has looked at it. Procurement members never see the Finance workspace, and the earlier version is kept in case anyone needs to check what the limit was before.
FAQ
Questions people ask
What is role-based access for business rules?
Role-based access for business rules means people get permissions based on their role, such as viewing, authoring or publishing decisions, rather than everyone having full control. It lets the business own its rules while keeping clear limits on who can put a change live.
What is business rules governance?
Business rules governance is how an organisation controls its rules: who owns each one, who can change it, how changes are tested and approved, and how past decisions are explained. Condexa supports it with workspaces, roles, versions and a trace for every run.
What roles are available in a Condexa workspace?
Members have roles such as viewer, author, publisher and owner. Viewers can look, authors can build and test, publishers can make a version Active, and owners manage the workspace and its members.
Can different teams keep their rules separate?
Yes. Each workspace holds its own workflows, lookup tables and lists, and only its members can see them. Finance, procurement and sales can each own their decisions without stepping on each other.
How do people sign in?
Through a secure identity provider. Members are invited into a workspace, and screens are permission-aware, so people only see the actions their role allows.
Keep exploring
Related decisions and guides
Features
Versioning
Nervous about changing a live rule? Draft it, test it, publish it, and keep every earlier version to fall back on.
Read moreProblems
Tribal knowledge
When only one person knows how a decision gets made, every holiday and every resignation is a risk.
Read moreTrust
Security
How Condexa protects your data and your decisions.
Read moreCompare
Condexa vs traditional BRMS
You need a rules engine, but not a year-long enterprise project. Compare Condexa with IBM ODM, Drools and similar.
Read moreHand the business its rules without handing over the keys
Bring a decision your team makes every week. We will build it with you, live, test it against your own examples and show your systems calling it.
No slides. Your decision, built live. No obligation.